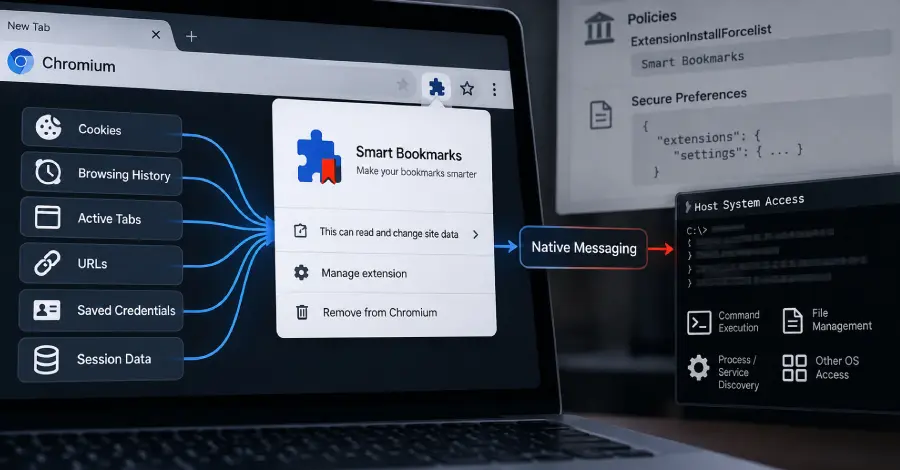
How PEEP Hijacks Browser Functionality
Cybersecurity researchers unveiled a sophisticated post‑exploitation tool, PEEP, that disguises itself as a harmless bookmarks extension for Chrome and Edge. The malware first requires administrative or code‑execution privileges to install, after which it injects the malicious extension directly into the browsers. Once active, PEEP grants attackers a covert command‑execution channel on the compromised host.
Latest news
 Corsair Vengeance DDR5-6000 Kit Offers Ideal Speed for AMD Builds
 Hide.me VPN releases major Android update
 Hackers launch massive PHP2Shell attack wave
 Googlebooks are not yet ready for prime time
The discovery highlights how attackers can exploit seemingly benign browser extensions to maintain persistence. By masquerading as a bookmarks manager, PEEP blends into normal user activity, avoiding detection by conventional security solutions. The tool’s architecture allows it to bypass typical extension vetting processes, leveraging the browsers’ privileged APIs to execute arbitrary commands on the underlying operating system.
What Can Users Do to Protect Themselves?
The injection process begins when an attacker gains initial foothold with elevated rights. The installer then modifies the browser’s extension directory, placing the PEEP payload in place of a legitimate bookmarks manager. Once the browser launches, the malicious extension loads automatically, establishing a hidden communication channel. This channel can receive commands from the attacker’s command‑and‑control server and execute them with the same privileges as the browser, effectively turning the web client into a remote control hub.
Security analysts noted that PEEP’s design takes advantage of the fact that many users install extensions from third‑party sites. The tool’s code is obfuscated, making static analysis difficult, and it uses encrypted communication to conceal its traffic. As a result, even advanced endpoint detection systems may miss the activity until the attacker begins executing system commands.
What Are the Long‑Term Implications for Browser Security?
The first line of defense is to restrict the installation of extensions to those vetted by official browser stores. Users should also monitor the list of installed extensions and remove any that appear suspicious or that they do not remember installing. Administrators can enforce policies that block the installation of extensions from unknown sources and enable browser security features that flag or quarantine suspicious code.
Regularly updating browsers and operating systems is also critical, as updates often patch vulnerabilities that tools like PEEP exploit. Finally, deploying endpoint protection that includes behavioral analysis can help detect the anomalous command‑execution patterns characteristic of this type of backdoor.
Frequently Asked Questions
The emergence of PEEP underscores a growing trend in cyber‑crime: turning everyday software into covert attack vectors. As browsers continue to serve as gateways to the internet, their extension ecosystems become increasingly attractive to threat actors. The incident suggests that future security models may need to incorporate stricter sandboxing and more transparent permission systems for extensions.
If attackers refine these techniques, we could see a shift toward more sophisticated, low‑visibility persistence mechanisms that bypass traditional security layers. Organizations will need to adopt a layered defense strategy, combining user education, policy enforcement, and advanced detection tools to mitigate the risk posed by such stealthy backdoors.
Comments
Leave a comment