Why the Vulnerabilities Persisted
A recent security alert has highlighted two medium‑severity vulnerabilities in the All‑In‑One SEO (AIOSEO) WordPress plugin, allowing attackers to compromise sites without authentication. The issues were discovered and reported in late September 2024, affecting versions 5.0.0 through 5.0.3. Site owners who have not updated the plugin are at risk of unauthorized data access and potential site takeover.
Latest news
 Corsair Vengeance DDR5-6000 Kit Offers Ideal Speed for AMD Builds
 Hide.me VPN releases major Android update
 Hackers launch massive PHP2Shell attack wave
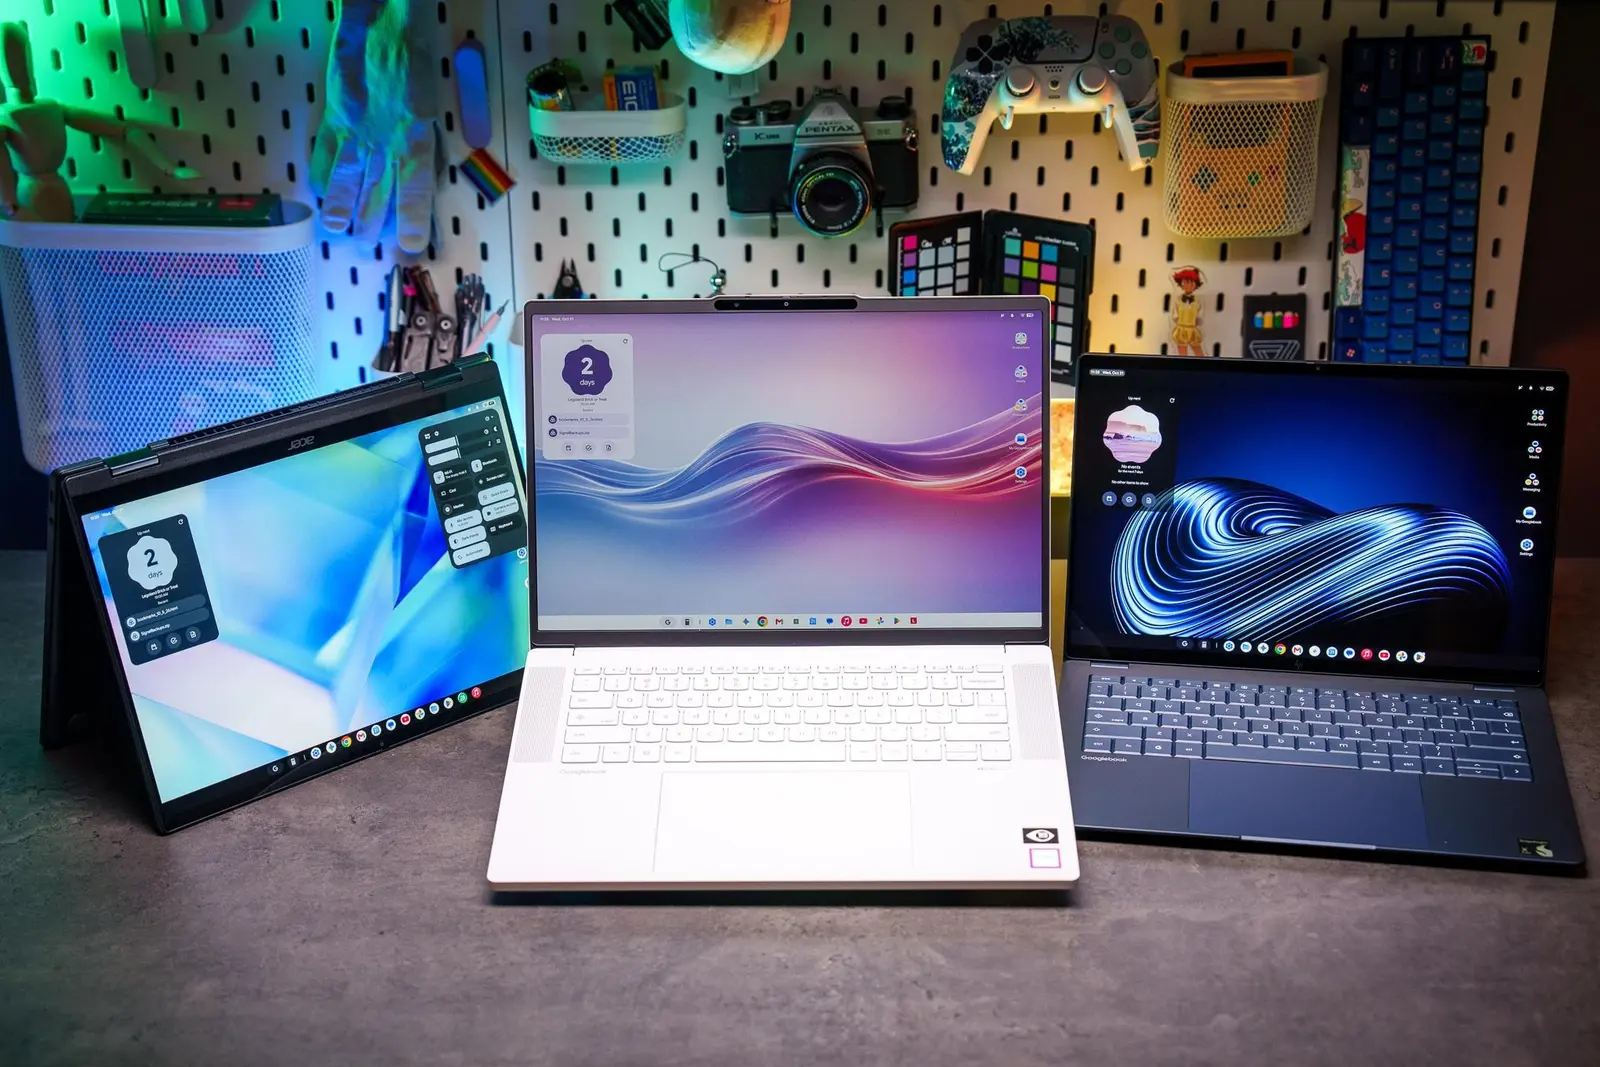 Googlebooks are not yet ready for prime time
The first flaw lies in the plugin’s „Meta Data” handling, where improperly sanitized input can lead to arbitrary file inclusion. An attacker can craft a request that forces the plugin to read server files outside the intended directory, exposing sensitive configuration or code. The second flaw concerns the „XML Sitemap” generator, which fails to validate user‑supplied URLs. This oversight permits attackers to inject malicious URLs that are then indexed by search engines, potentially facilitating phishing or malware distribution. Both exploits require no user credentials and can be executed by sending a single crafted HTTP request.
How Site Owners Can Protect Themselves
Security researchers noted that the AIOSEO development team had released a patch for the first issue in early September, but the second flaw was overlooked until a third‑party audit identified it. The oversight stemmed from a recent refactor of the sitemap module, where developers removed input validation to improve performance. The lack of regression testing allowed the flaw to slip into production releases. AIOSEO’s response emphasized a commitment to rapid patching and urged site administrators to upgrade to version 5.0.4, which includes comprehensive input sanitization and stricter file handling.
Is Your Site at Risk? How
The most immediate remedy is to update the plugin to the latest stable release. WordPress users can do this via the dashboard, or by downloading the new version from the official repository. Site administrators should also review their security configurations: enable the built‑in „Security” settings in AIOSEO, restrict file permissions on the WordPress root, and consider using a Web Application Firewall to block suspicious traffic. Regular backups remain essential; if an attacker succeeds, a recent backup can restore the site to a pre‑compromise state.
Frequently Asked Questions
Site owners can quickly determine whether they are affected by running a simple test. By navigating to the site’s XML sitemap URL (usually /sitemap.xml) and inspecting the header, users can verify if the sitemap generation script is the vulnerable version. Alternatively, using a command‑line tool like curl to request the sitemap and analyze the response can reveal the presence of the flaw. If the sitemap contains unexpected URLs or the request fails with a 500 error, the site likely needs an update. For those unsure, contacting a professional WordPress security consultant can provide a thorough audit.
The vulnerabilities underscore the importance of timely updates and rigorous testing in the WordPress ecosystem. While the flaws are medium‑severity, their exploitation could lead to data leakage or malicious content injection, affecting search rankings and user trust. The AIOSEO team has pledged to release a comprehensive security guide and will monitor for any new threats. Site owners who remain on older plugin versions may face increased exposure, so immediate action is advised.
Comments
Leave a comment