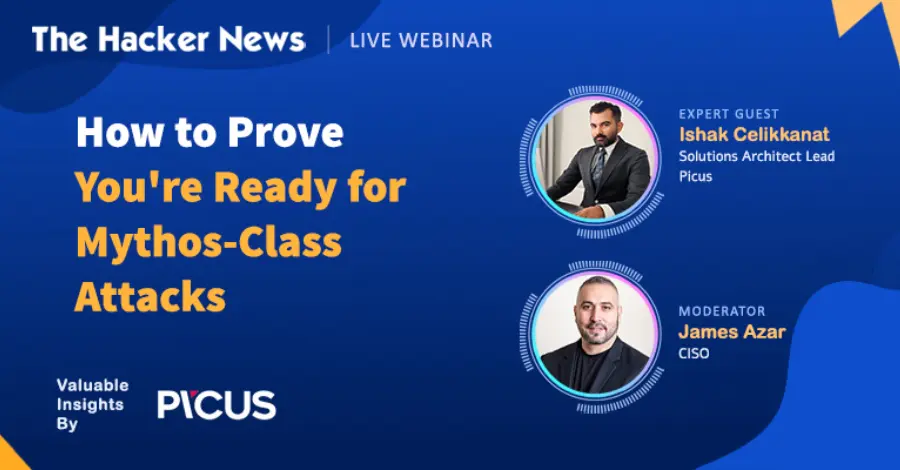
Closing the Gap Between Discovery and Defense
Security teams face a critical challenge when new vulnerabilities emerge daily. Automated scanners often flag high-severity issues, but these scores fail to clarify if a specific flaw poses an immediate risk to a unique corporate network. Determining actual exploitability remains the most urgent task for defenders in an era of rapid cyber threats.
Latest news
 YouTube is tightening rules for low-effort Shorts
 Google releases Android 17 QPR 3 Beta 1 for testing
 Samsung Galaxy S26 FE Slashes $40 Off Its Launch Price
 Meta Launches Muse Gadgets to Bring Brain-Sensing Tech to DIY Hardware
Modern security operations struggle to keep pace with attackers who leverage advanced artificial intelligence to weaponize vulnerabilities. This technological shift compresses the window between a public disclosure and a functional exploit. Consequently, traditional patching methods often fall behind, leaving critical systems exposed to automated attacks that bypass standard defensive perimeters.
The primary obstacle for security professionals is the disconnect between vulnerability scanners and real-world threat intelligence. A high severity rating does not automatically translate into an imminent breach. Defenders must evaluate whether the vulnerable component is reachable, active, or protected by existing security controls within their specific infrastructure.
Can Predictive Analysis Neutralize Emerging Threats?
Experts suggest that organizations must shift from reactive patching to proactive risk modeling. By simulating attack paths, security teams can identify which vulnerabilities are truly reachable by adversaries. This approach allows IT departments to focus their limited resources on the flaws that present the highest probability of being weaponized against their systems.
The integration of threat intelligence with internal asset data is essential for modern risk management. When security teams understand the specific mechanics of a vulnerability, they can implement compensating controls even before a vendor patch becomes available. This strategy minimizes the attack surface and provides a vital buffer during the critical hours following a disclosure.
Frequently Asked Questions
Failure to distinguish between theoretical risk and actual exploitability leads to patch fatigue and operational inefficiencies. As attackers continue to refine their automated toolsets, the ability to rapidly assess and prioritize threats will define the effectiveness of corporate security programs. Organizations that master this predictive capability will significantly reduce their likelihood of a successful compromise.
What makes current vulnerability management ineffective? Traditional scanners prioritize flaws based on generic severity scores rather than environmental context. This often leads to wasted effort on vulnerabilities that are not actually reachable by attackers.
How does artificial intelligence change the threat landscape? AI allows attackers to develop working exploits much faster than in the past. This acceleration forces security teams to move beyond manual analysis to keep up with the pace of modern cyber threats.
Comments
Leave a comment