How AI Is Shortening the Exploit Development Cycle
Security researchers uncovered that four distinct hacking collectives leveraged the same exploit kit targeting unpatched flaws in Chrome and Windows during coordinated attacks observed over several days in early September 2026. The activity was detected through telemetry from endpoint protection platforms monitoring enterprise networks across North America and Europe. The exploit kit combined a use-after-free vulnerability in Chrome’s V8 JavaScript engine with a privilege escalation flaw in Windows Kernel Cryptography drivers, allowing attackers to bypass sandbox protections and execute arbitrary code with system-level privileges. All four groups deployed the toolkit within a 72-hour window, suggesting either shared access to a private exploit marketplace or rapid independent discovery following public disclosure of the underlying bugs.
Latest news
 Corsair Vengeance DDR5-6000 Kit Offers Ideal Speed for AMD Builds
 Hide.me VPN releases major Android update
 Hackers launch massive PHP2Shell attack wave
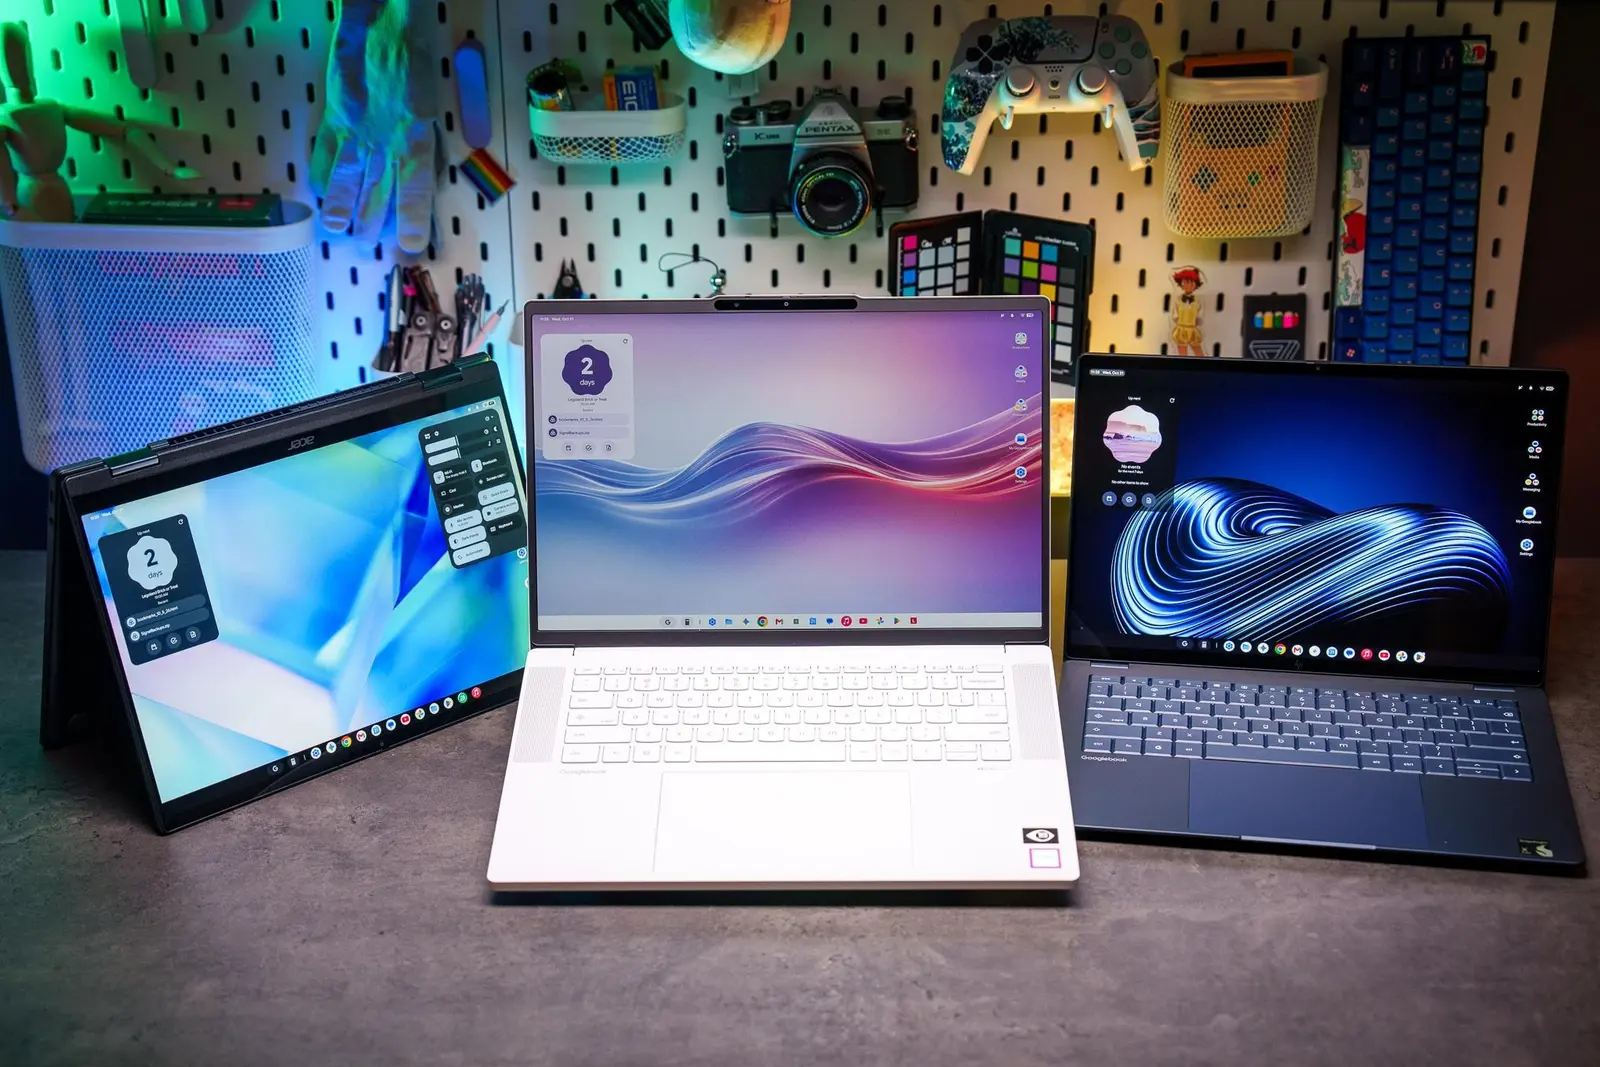 Googlebooks are not yet ready for prime time
The simultaneous use highlights a growing gap between vulnerability disclosure and patch deployment, exacerbated by accelerated AI-driven threat intelligence Analysis indicates that the window between public disclosure of the Chrome and Windows flaws and widespread patch adoption averaged 18 days across affected organizations, well beyond the recommended 72-hour emergency timeline. This delay was attributed to complex dependency testing in legacy enterprise environments and staggered update cycles in critical infrastructure sectors. Simultaneously, AI-powered vulnerability scanning tools used by both defensive teams and threat actors have reduced the time to identify exploitable conditions from weeks to hours, creating a race where attackers often weaponize flaws before defenders can fully assess risk. One anonymous source from a major cloud security firm noted that „the asymmetry in exploit development speed is now measured in hours, not days,” urging vendors to prioritize exploit likelihood over severity scores in patch prioritization frameworks.
What Can Organizations Do to Close the Patch Gap?
Machine learning models trained on historical exploit patterns and code repositories are now capable of predicting exploitability with over 85% accuracy within hours of a CVE publication, according to a 2026 study by the Institute for Digital Defense. These tools analyze control flow graphs, memory safety violations, and exploit primitive chaining to generate proof-of-concept code automatically. While defenders use similar systems to prioritize patching, threat actors leverage them to identify low-effort, high-impact targets. In this case, the AI-generated exploit chains required minimal modification to bypass modern mitigations like Control Flow Guard and Arbitrary Code Guard, indicating that current defenses struggle to keep pace with automated attack generation. Researchers warn that without corresponding advances in runtime protection and automated patch validation, the exploit window will continue to shrink.
Enterprises are advised to adopt AI-assisted patch validation platforms that simulate exploit behavior in isolated environments before deployment, reducing testing time from days to hours. Implementing zero-trust network segmentation and enforcing browser isolation for high-risk web traffic can limit lateral movement even if initial compromise occurs. Additionally, sharing exploit telemetry through trusted information sharing and analysis centers (ISACs) allows faster collective response when multiple groups target the same vulnerability. Regulatory bodies in the EU and US are considering mandates for critical sectors to report patch latency metrics, aiming to create accountability for delayed updates. Until then, the race between automated discovery and human-driven defense will remain heavily tilted toward attackers unless defensive automation matures at equal speed.
How did four different groups obtain the same exploit kit? Investigators believe the groups either accessed a shared private exploit marketplace or independently developed similar tools using publicly available vulnerability details and AI-assisted code generation techniques, which have lowered the barrier to exploit creation.
Frequently Asked Questions
Why weren’t the patches applied faster despite known risks? Delayed patching stemmed from lengthy compatibility testing in complex IT environments, particularly in healthcare and manufacturing sectors, where system updates require extensive validation to avoid operational disruption.
Are Chrome and Windows still vulnerable to this specific exploit chain? No, patches for both the Chrome V8 flaw (CVE-2026-4821) and Windows Cryptography driver issue (CVE-2026-4822) were released in late August 2026 and are effective when applied; however, unpatched systems remain at risk.
Comments
Leave a comment