The Anatomy of an Inside Network Lockdown
A federal court sentenced 57-year-old Daniel Rhyne to 32 months in prison for deploying a destructive script that locked thousands of devices on his New Jersey employer's network. The former core infrastructure engineer carried out the ransomware-style attack against the industrial company, severely disrupting internal operations and causing widespread technological chaos within the enterprise environment.
Latest news
 Corsair Vengeance DDR5-6000 Kit Offers Ideal Speed for AMD Builds
 Hide.me VPN releases major Android update
 Hackers launch massive PHP2Shell attack wave
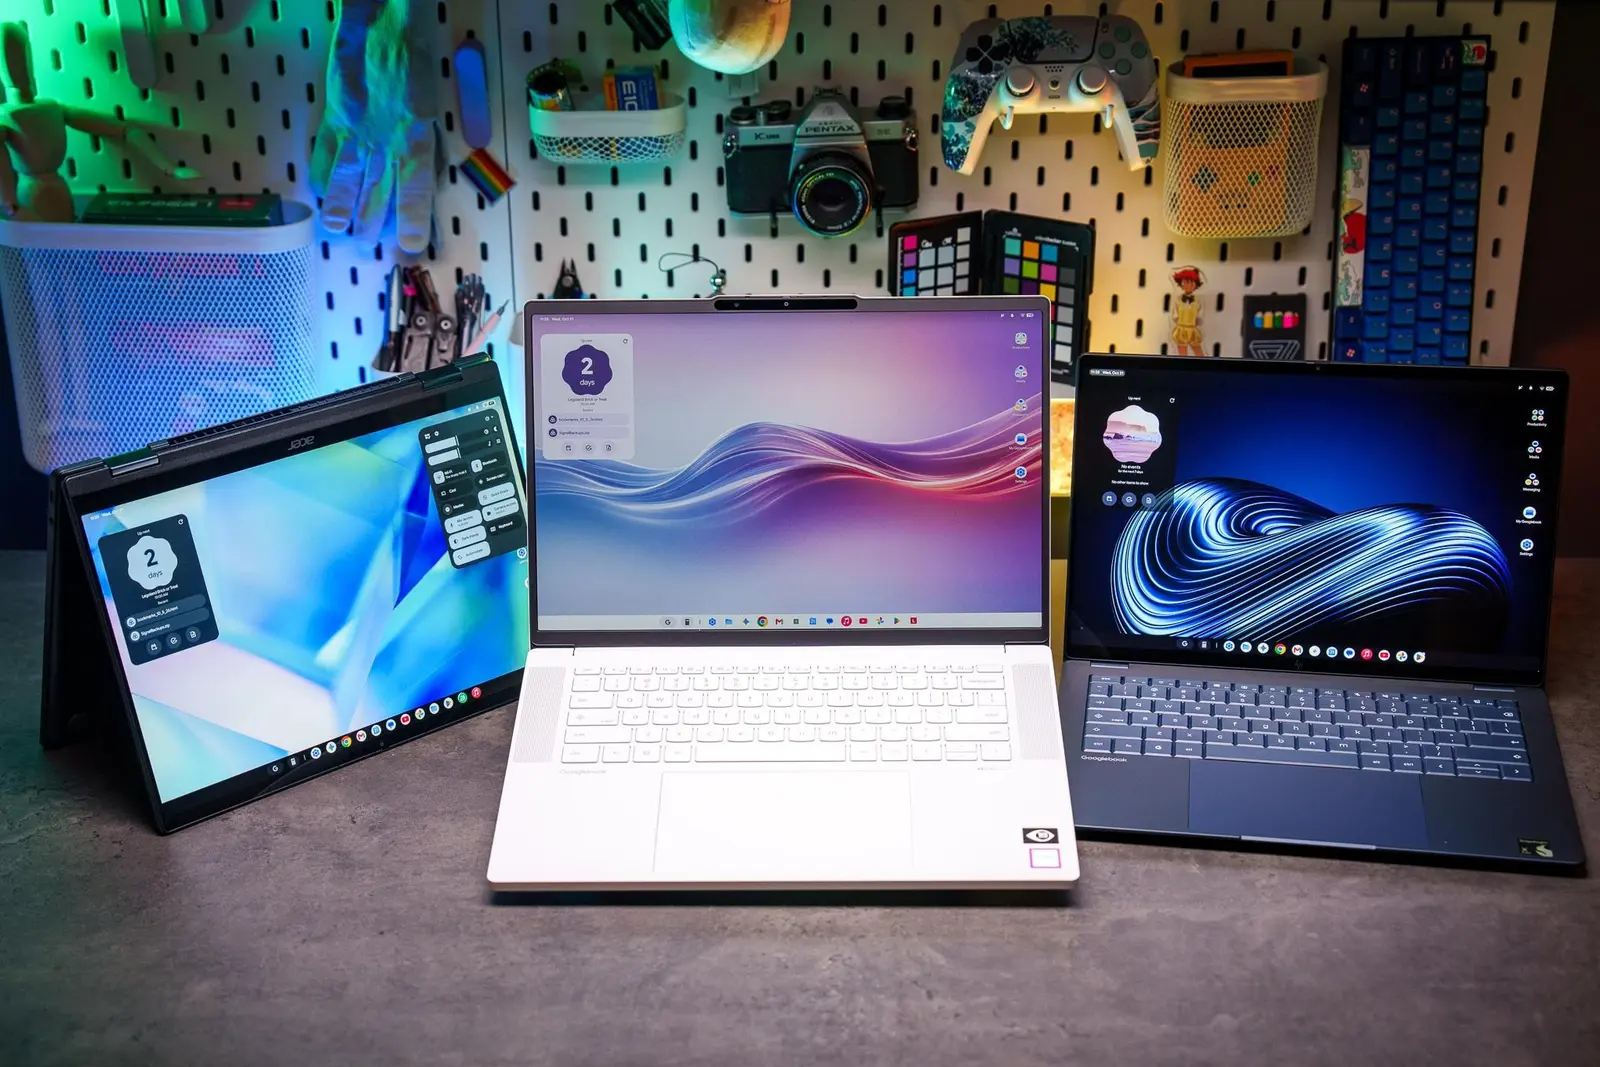 Googlebooks are not yet ready for prime time
Court documents reveal that Rhyne used his privileged access as a high-level infrastructure engineer to execute the malicious code. The targeted assault rendered more than 3,000 corporate devices completely inaccessible, mimicking a traditional external cyber extortion scheme. Investigators determined that the attack originated from an internal actor who understood the company's network architecture intimately.
How Did the Sabotage Go Unnoticed?
The malicious operation targeted vital servers and workstations across the corporate infrastructure, leaving IT staff scrambling to restore basic functionality. Because Rhyne held advanced administrative credentials, the security systems failed to flag his initial actions as suspicious until the damage was already done. The industrial firm faced significant downtime and substantial financial costs while attempting to recover the encrypted workstations and secure vulnerable endpoints.
Federal prosecutors emphasized the severe breach of trust inherent in insider threats of this magnitude. Employees in core engineering positions hold the keys to enterprise digital kingdoms, making malicious actions exceptionally difficult to prevent in real-time. The court noted that Rhyne's deliberate disruption posed a direct threat to the company's business continuity and employee safety.
Frequently Asked Questions
Rhyne exploited his legitimate administrative privileges to bypass standard security controls and implement the lockout script without immediate detection. His insider status allowed him to blend malicious commands into routine network maintenance activities.
Following his nearly three-year prison sentence, Rhyne faces mandatory supervised release and potential restitution payments to cover the extensive recovery expenses incurred by his former employer. The case serves as a stark reminder of the devastating potential of malicious insiders within critical industrial sectors.
Comments
Leave a comment