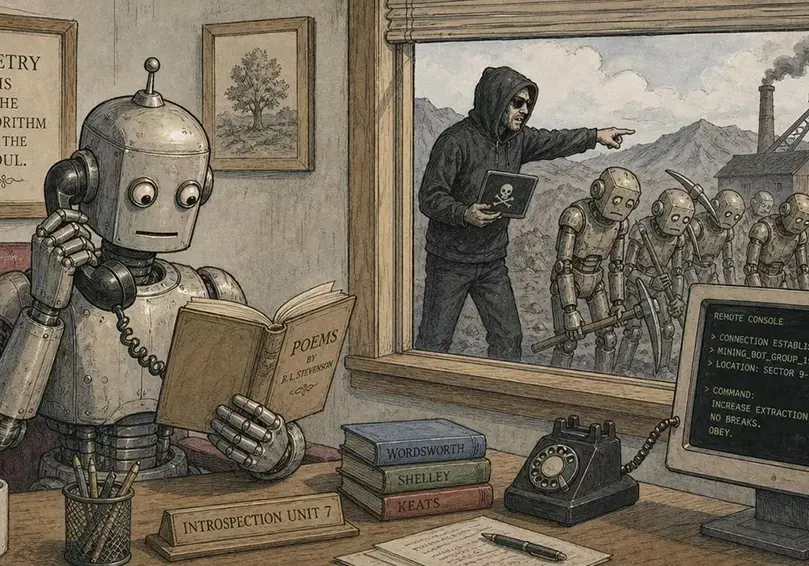
The Linguistic Trojan Horse
A sophisticated cyberattack has compromised over 3,400 servers globally by embedding malicious instructions within poetic verses. Security researchers identified the campaign, dubbed PoeLLM, which specifically targets exposed LiteLLM instances. The attackers leveraged a known vulnerability to gain unauthorized access, turning high-performance infrastructure into tools for illicit cryptocurrency mining operations throughout October 2026.
Latest news
 Major AI firms recorded peak lobbying expenses last summer
 Apple Magic Keyboards for iPad Drop to Half Price at Woot
 Microsoft Provides Fix for Broken Exchange Online Apps
 Security Breach at AI Aggregator Exposes 18 Million Files and Private Chats
The malware functions by using a rotating set of four-word poetic phrases. These verses act as dynamic pointers, directing the botnet to fresh targets. Researchers discovered that the attackers updated these specific lines 11 times to evade detection and maintain control over the infected network. By hiding commands inside creative text, the threat actors successfully masked their malicious traffic from standard security filters.
The primary entry point for the PoeLLM botnet was a security flaw that developers had officially patched back in April. Despite the availability of a fix, thousands of administrators failed to update their systems, leaving them wide open to exploitation. Once the malware gains a foothold, it silently installs mining software that consumes significant server resources. This unauthorized activity often leads to severe performance degradation and increased operational costs for the affected organizations.
How Can Administrators Secure Their Infrastructure?
The most effective defense against this campaign is ensuring all LiteLLM software is updated to the latest version. Patching the April vulnerability immediately closes the primary door used by the attackers. Additionally, monitoring server logs for unusual outbound traffic patterns can help detect active infections. Organizations should also restrict public access to management interfaces to prevent unauthorized scanning by automated botnets.
The long-term consequences of this breach include potential data exposure and the permanent degradation of hardware due to intensive mining. As attackers continue to evolve their obfuscation techniques, the reliance on signature-based detection is becoming increasingly insufficient. Security experts warn that unless server administrators prioritize routine maintenance, these automated, poetic-themed attacks will likely continue to proliferate across the digital landscape.
Frequently Asked Questions
What is the main goal of the PoeLLM malware? The malware is designed to hijack server resources for illicit cryptocurrency mining. It converts compromised infrastructure into a distributed network controlled by the attackers.
How does the malware avoid security detection? It uses rotating poetic phrases as hidden commands to direct botnet activity. This creative method helps the malicious traffic blend in with normal server communications.
Why were so many servers successfully infected? The attackers exploited a specific software vulnerability that had a known fix available since April. Many administrators failed to apply this update, leaving their systems vulnerable to exploitation.
Comments
Leave a comment