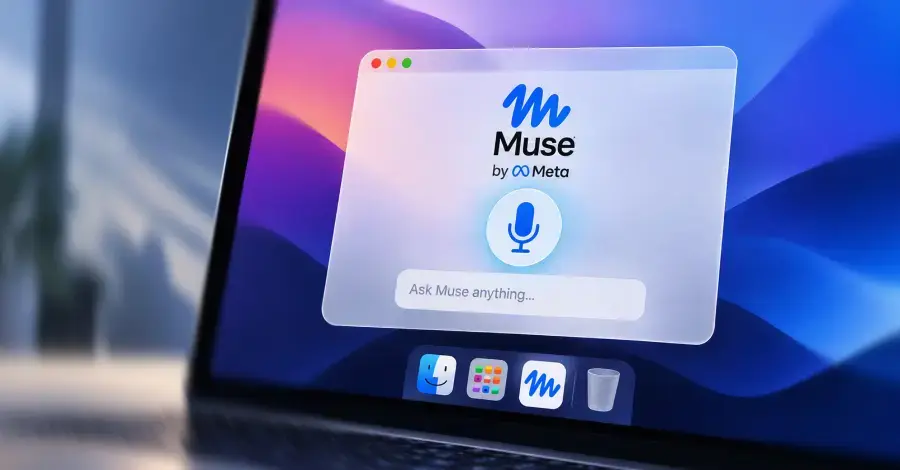
Exploiting Deep System Permissions
Security researcher Patrick Wardle revealed a novel attack vector on September 21, demonstrating how malware already active on a macOS system can silently hijack Meta's Muse AI assistant. The exploit misuses the deep permissions granted to the AI tool, transforming a helpful productivity utility into a covert digital backdoor for malicious actors.
Latest news
 YouTube is tightening rules for low-effort Shorts
 Google releases Android 17 QPR 3 Beta 1 for testing
 Samsung Galaxy S26 FE Slashes $40 Off Its Launch Price
 Meta Launches Muse Gadgets to Bring Brain-Sensing Tech to DIY Hardware
The technique relies on stealthily altering a buried preference setting within the application. Once this configuration is flipped, the malicious software can piggyback on the assistant whenever the owner interacts with the system. Because users typically grant AI assistants extensive access to files, applications, and personal data, this hijacked channel gives intruders free rein across the compromised machine.
How Can Users Protect Their Systems?
Modern artificial intelligence tools require broad capabilities to function effectively, bridging the gap between local user files and cloud intelligence. Wardle's proof-of-concept highlights the inherent dangers of these expansive permissions when security boundaries fail. Rather than breaking through traditional defenses, the malware simply redirects the trusted assistant's existing privileges for illicit objectives.
The attack unfolds entirely in the background without raising immediate red flags for the device owner. Since the AI application is a legitimate, authorized tool, standard security monitors often overlook its unusual behavior. This silent takeover underscores a growing blind spot in endpoint protection as intelligent assistants become deeply embedded in everyday desktop environments.
Defending against this specific threat requires strict vigilance regarding endpoint security and malware prevention on macOS devices. Because the exploit demands that malicious code is already running on the computer, stopping initial infection vectors remains the primary line of defense. Users should regularly audit application permissions and monitor background configuration changes in sensitive system directories.
Frequently Asked Questions
As artificial intelligence integration expands across consumer operating systems, securing the communication channels between users, AI tools, and local data will become critical. Researchers like Wardle continue to expose these architectural vulnerabilities to push technology companies toward stricter isolation protocols. Ultimately, ensuring that helper applications cannot be subverted by localized malware is vital for maintaining user trust in desktop AI.
Q: Who discovered this vulnerability and when was it made public? A: Security researcher Patrick Wardle released the proof-of-concept demonstration on September 21, highlighting the hidden setting manipulation.
Comments
Leave a comment