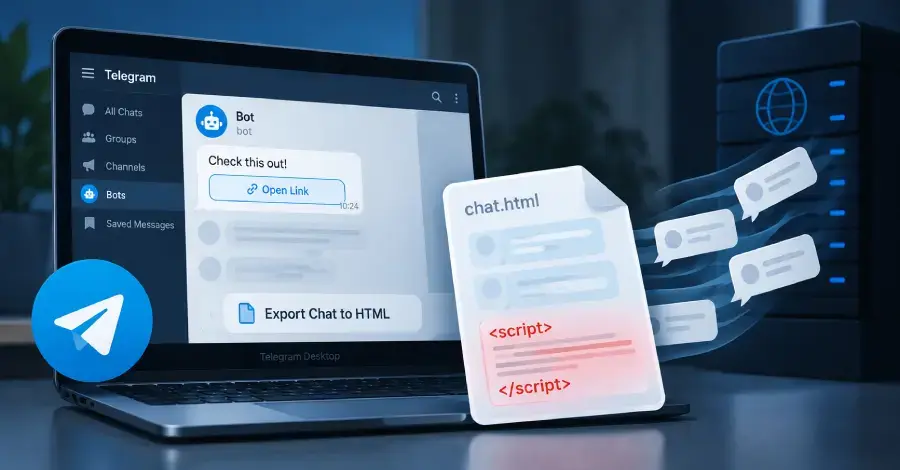
How the Attack Evaded Detection in Telegram
A security vulnerability in Telegram Desktop enabled malicious bots to inject hidden JavaScript into chat messages, which could exfiltrate user data when the chats were exported as HTML files. Researchers from ExPatch disclosed the flaw on September 12, 2026, noting that the attack required no user interaction beyond exporting a conversation. The malicious script remained dormant until the HTML file was opened in a web browser, at which point it could access and transmit message contents to an external server. The vulnerability affected versions of Telegram Desktop prior to the patch released in mid-September 2026.
Latest news
 Major AI firms recorded peak lobbying expenses last summer
 Apple Magic Keyboards for iPad Drop to Half Price at Woot
 Microsoft Provides Fix for Broken Exchange Online Apps
 Security Breach at AI Aggregator Exposes 18 Million Files and Private Chats
The exploit worked by embedding a seemingly innocuous link button within a bot-generated message. While the message appeared normal in the Telegram interface, the underlying HTML contained a script tag designed to execute when the exported file was rendered in a browser. Once activated, the script could read the entire chat history from the exported file and send it to a remote endpoint controlled by the attacker. ExPatch researchers emphasized that the attack chain relied on the user’s decision to export a chat and subsequently open the resulting HTML file, making it a targeted but feasible threat for individuals handling sensitive conversations.
Could This Affect Other Platforms Using Similar Export Functions?
The malicious JavaScript was concealed within the message’s metadata using a technique that bypassed Telegram’s standard content sanitization for exported chats. Although the platform filters out active scripts in real-time messaging, the export function did not apply the same level of scrutiny to HTML output, allowing the payload to persist. According to ExPatch, the script used obfuscation tactics to avoid triggering basic security heuristics, making it difficult to detect without manual code inspection. Researchers noted that the flaw highlighted a gap between Telegram’s in-app security measures and the safety of its data export features, particularly for users who archive chats for backup or legal purposes.
While the vulnerability was specific to Telegram Desktop’s HTML export mechanism, experts warn that similar risks may exist in other messaging apps that allow chat exports without rigorous script sanitization. The incident underscores the importance of treating exported data as potentially active content, especially when shared or opened in untrusted environments. Telegram has since patched the issue by implementing stricter content filtering during the export process, ensuring that scripts are stripped before file generation. Users are advised to update to the latest version of Telegram Desktop and exercise caution when opening exported chat files from unknown sources.
How did attackers deliver the malicious JavaScript? Attackers used bot accounts to send messages containing hidden script tags that appeared as regular links in Telegram but executed when the chat was exported to HTML and opened in a browser.
Frequently Asked Questions
Is my data at risk if I haven’t exported any chats? No, the vulnerability only posed a risk when users exported chats to HTML format and subsequently opened those files in a web browser. Regular use of Telegram remains unaffected.
What should I do if I exported a chat before the patch? Delete any exported HTML files from before mid-September 2026 and avoid opening them. Update Telegram Desktop to the latest version to prevent future exposure.
Comments
Leave a comment