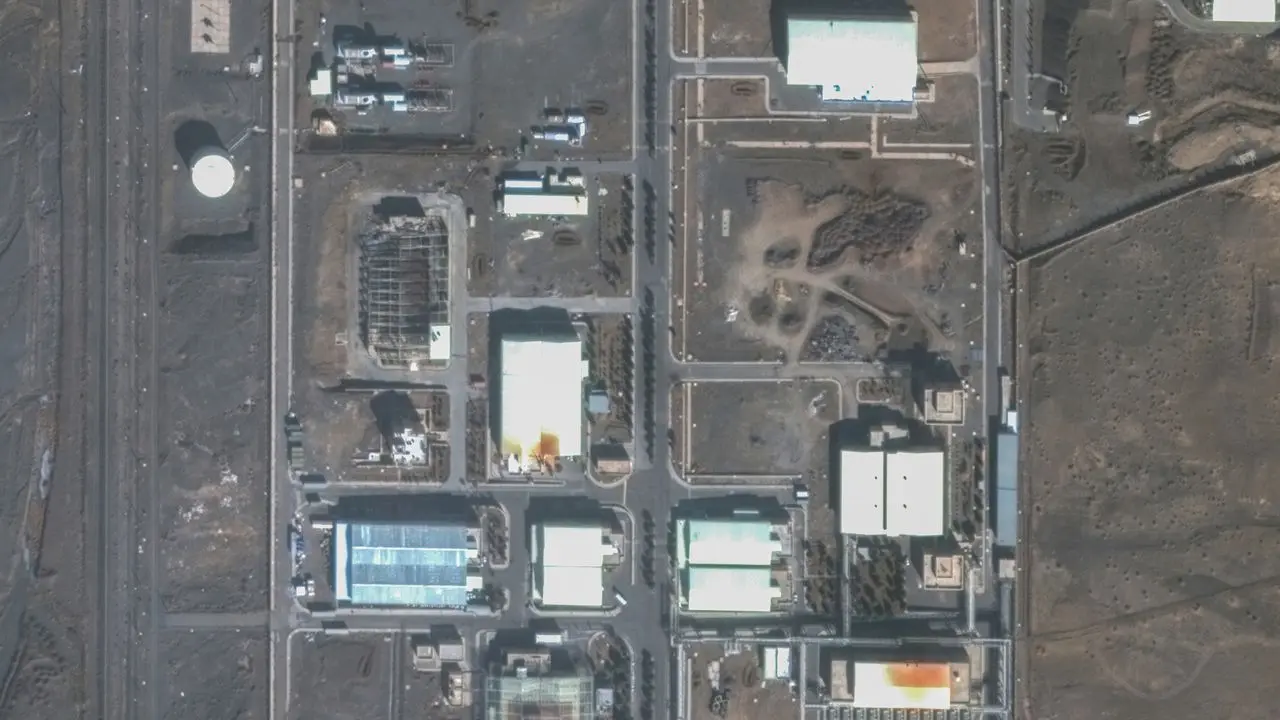
Decoding the Logic Behind Physical Damage
An anonymous security researcher has successfully reverse-engineered the source code of the Stuxnet worm. The complex piece of malware was originally designed to target Iranian nuclear facilities. The researcher published the reconstructed code on GitHub, making it available to the public. This release allows developers and analysts to study one of history’s most sophisticated cyberattacks. The work provides rare insight into how digital weapons can affect physical infrastructure.
Latest news
 Anker Unveils Playful 45W Charger With Animated Face Display
 Google Docs Web Version Still Missing Native Dark Mode
 Anthropic-Linked Vulnerability Exploited From China, Targets US and Japan
 Text‑Based AI Agents: Your New Digital Assistants
Stuxnet emerged in 2010 as a joint effort between the United States and Israel. Its primary goal was to slow down Iran’s uranium enrichment program. The worm specifically targeted Siemens PLC systems used in centrifuges. It manipulated the speed of the machines while reporting normal data to operators. This deception caused physical wear and tear on the equipment. The attack demonstrated that software could cause tangible damage to hardware.
The newly released code reveals the intricate logic Stuxnet used to confuse industrial control systems. The malware contained multiple layers of encryption and obfuscation. These features made it extremely difficult to analyze without specialized tools. The researcher spent significant time mapping out these complex structures. The code included specific commands to alter the rotation speed of centrifuges. It would spin them faster than their rated limits, then slower. This stress testing eventually led to mechanical failure. The release highlights the precision required to build such a targeted weapon.
What Does This Release Mean for Cybersecurity?
Researchers note that Stuxnet was the first known malware to bridge the gap between IT and OT networks. It exploited zero-day vulnerabilities in Windows operating systems. It also targeted specific firmware in Siemens controllers. The dual-target approach ensured the worm could spread widely before hitting its mark. The published code now serves as a reference for modern cybersecurity teams. They can use it to understand how similar threats might evolve.
The availability of the source code invites scrutiny from the global tech community. Experts can now verify previous assumptions about the worm’s behavior. Some analysts believe this transparency will help secure modern industrial systems. By understanding the past, engineers can better protect current infrastructure. However, there is a slight risk that attackers could learn new tricks. They might use the code as a template for future attacks. Despite this, the educational value outweighs the potential risks for most experts.
The release underscores the lasting impact of state-sponsored cyber warfare. Stuxnet changed how nations view digital assets. It proved that software is a strategic tool in geopolitical conflicts. As industrial systems become more connected, the threat landscape expands. The open-source release of Stuxnet marks a milestone in cybersecurity history. It transforms a classified secret into a shared resource. This shift encourages collaborative defense strategies worldwide.
Frequently Asked Questions
Who released the Stuxnet source code? An anonymous security researcher published the reconstructed code on GitHub. The individual worked independently to reverse-engineer the original binary files.
When did the original Stuxnet attack occur? The malware first appeared in 2010. It primarily targeted nuclear facilities in Iran during that period.
Why is this release significant? It provides the public with access to the first malware to cause physical damage. This allows for deeper analysis of its mechanisms and impacts.
Comments
Leave a comment