How the Attacks Were Carried Out
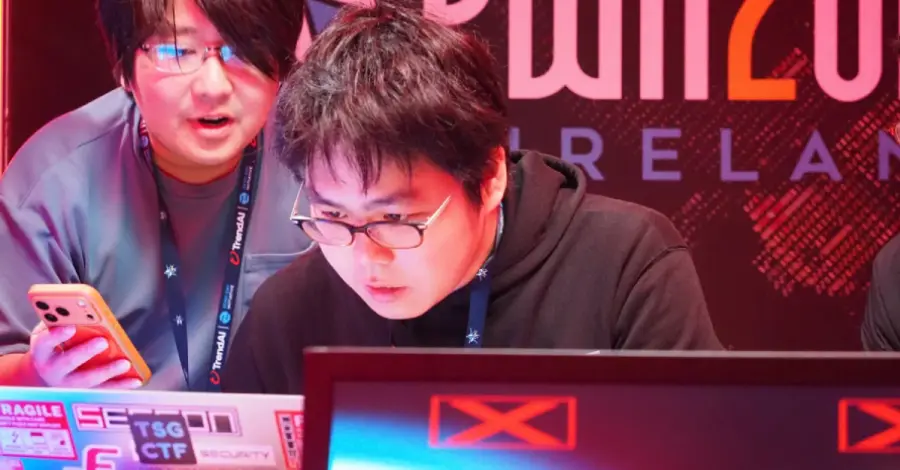
Three independent security researchers succeeded in breaching a Google Pixel 10 device on October 8 during the Pwn2 Own competition in Cork, Ireland. The event, known for its strict requirement that all target devices be fully patched, offers monetary rewards for demonstrable exploits that are then reported to the vendor for remediation.
Latest news
 Major AI firms recorded peak lobbying expenses last summer
 Apple Magic Keyboards for iPad Drop to Half Price at Woot
 Microsoft Provides Fix for Broken Exchange Online Apps
 Security Breach at AI Aggregator Exposes 18 Million Files and Private Chats
The Pixel 10, released by Google earlier this year, had received the latest security updates before the contest. Despite this, the researchers identified and leveraged vulnerabilities that allowed them to execute code remotely. Each team demonstrated a separate attack vector, showcasing the range of potential weaknesses in even the most up-to-date Android devices.
The first exploit involved a flaw in the device’s camera subsystem. By sending a crafted image file, the attacker was able to trigger a buffer overflow that granted arbitrary code execution. The second team targeted the Bluetooth stack, exploiting a race condition that permitted unauthorized access to the device’s data. The third attack focused on the system’s kernel, using a privilege escalation bug that bypassed sandbox restrictions. All three exploits required no physical access and could be initiated from a distance, highlighting the severity of the findings.
What Does This Mean for Mobile Security?
Google’s response was swift. Within hours of the demonstrations, the company issued a patch that addressed the identified vulnerabilities. The patches were subsequently added to the next security update rollout, ensuring that Pixel 10 users receive the fix without delay. The competition’s organizers praised the researchers for their professionalism and adherence to responsible disclosure practices.
The incidents underscore that even heavily patched devices can harbor critical flaws. Security teams must maintain rigorous testing protocols, including fuzzing and formal verification, to uncover hidden weaknesses. For consumers, the takeaway is clear: keeping devices updated is essential, but it does not guarantee immunity from sophisticated attacks.
The Pwn2 Own event continues to be a proving ground for security researchers, and this year’s results reaffirm the importance of independent verification. As mobile operating systems grow more complex, the likelihood of undiscovered vulnerabilities increases, making such competitions vital for the ecosystem’s safety.
Frequently Asked Questions
Q1: How long did it take the researchers to develop their exploits? A1: Each team spent several weeks researching the Pixel 10’s architecture. The actual exploitation code was written in a matter of hours once the target vulnerability was identified.
Q2: Will the new patches affect device performance? A2: Google states that the updates are lightweight and designed to avoid any noticeable impact on performance or battery life.
Q3: Are other Google devices at risk? A3: The vulnerabilities were specific to the Pixel 10’s implementation. However, similar weaknesses could exist in other models, emphasizing the need for continuous security reviews across the product line.
Comments
Leave a comment