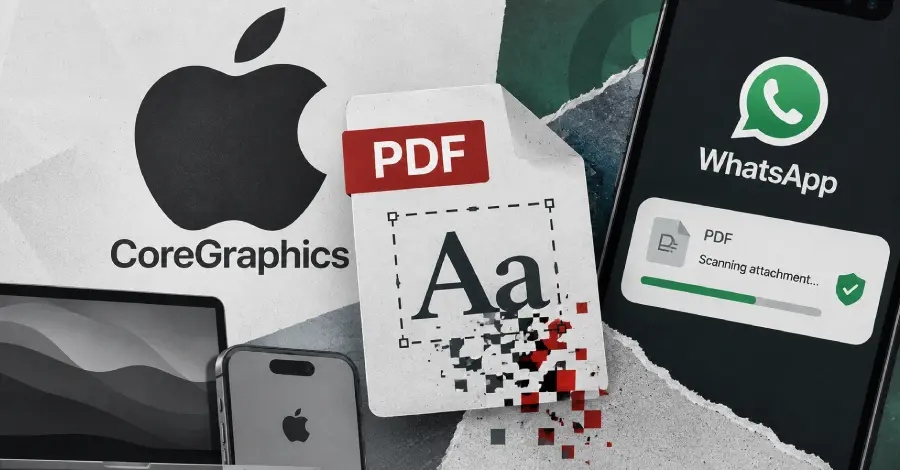
Mechanics of the PDF Font Exploit
Security researchers have released a public proof-of-concept for CVE-2026-86950, a critical vulnerability affecting Apple’s CoreGraphics framework. This flaw, which Apple warns has already been exploited in targeted attacks, allows attackers to crash unpatched i Phones by sending a malicious PDF file containing a specially crafted embedded font.
Latest news
 Why the Rumored iPhone Duo Excites Android Foldable Fans
 AMD's Canceled Ryzen 9 5900X3D Leaks Online
 California Subpoenas OpenAI Over Autonomous AI Hacking Risks
 Nvidia-Backed UK Supercomputer Faces Multi-Year Power Delay
The vulnerability resides in how the CoreGraphics library processes font data within PDF documents. When a compromised device opens such a file, the system fails to handle the malicious font structure, leading to a system crash. Experts suggest that attackers may be utilizing WhatsApp’s document delivery mechanism to distribute these weaponized files to unsuspecting targets.
The exploit functions by manipulating the font rendering process deep within the operating system. By embedding a malformed font object, the attacker forces the device to execute unauthorized operations during the parsing phase. This bypasses standard security checks that are intended to validate incoming document data.
Could Your Device Be at Risk?
Because the vulnerability triggers upon the simple act of opening a document, it provides a highly effective vector for malicious actors. Security analysts remain concerned that the release of a functional proof-of-concept will lower the barrier for entry, allowing less sophisticated attackers to replicate these targeted strikes against a broader range of users.
The primary defense against this exploit is immediate software remediation. Apple has already issued patches to address the underlying memory corruption issues within the CoreGraphics framework. Users who have not updated their devices remain vulnerable to potential remote code execution or persistent system instability if they encounter a malicious file.
Security firms are currently monitoring the situation to see if the exploit code is integrated into broader malware campaigns. While the current proof-of-concept is intended for research purposes, the existence of such tools often precedes a surge in real-world exploitation attempts. Users are urged to verify their system version and apply all pending security updates immediately.
Frequently Asked Questions
What is the primary danger of this vulnerability? The flaw allows an attacker to crash an i Phone simply by sending a malicious PDF. If weaponized further, it could potentially lead to unauthorized code execution.
How can users protect their i Phones from this threat? The most effective protection is to install the latest iOS security updates provided by Apple. Keeping your device updated ensures that the CoreGraphics library is patched against known exploits.
Is this vulnerability being used in active attacks? Yes, Apple has confirmed that this flaw has been utilized in targeted attacks against specific individuals. The public release of the proof-of-concept increases the risk that these attacks could expand.
Comments
Leave a comment