Technical Details and Exploitation Method
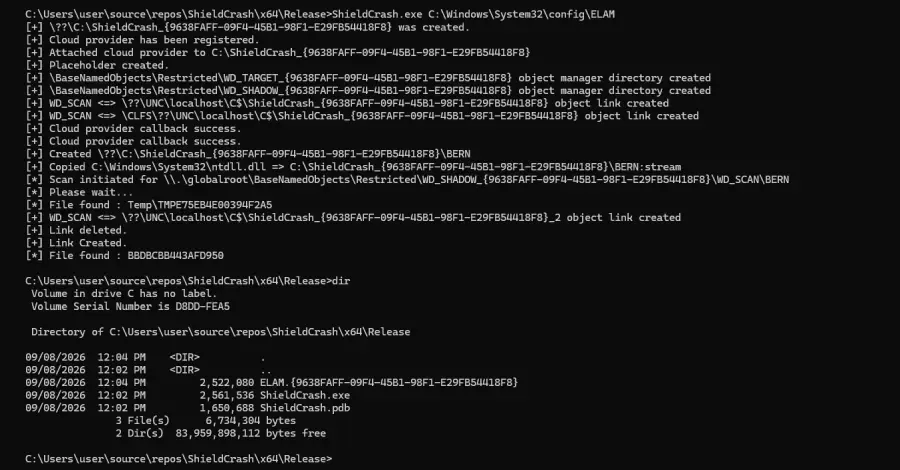
Security researcher Chaotic Eclipse has published a proof-of-concept exploit targeting Microsoft Defender, demonstrating a bypass of a previously patched vulnerability. The newly discovered flaw, labeled ShieldCrash, affects the same component addressed in CVE-2026-69414, known as ShieldBreak, which carries a CVSS score of 7.8. The PoC was released on September 9, 2026, highlighting ongoing weaknesses in Microsoft's endpoint protection platform.
Latest news
 Why the Rumored iPhone Duo Excites Android Foldable Fans
 AMD's Canceled Ryzen 9 5900X3D Leaks Online
 California Subpoenas OpenAI Over Autonomous AI Hacking Risks
 Nvidia-Backed UK Supercomputer Faces Multi-Year Power Delay
The ShieldBreak vulnerability was originally patched earlier this year after being flagged as a critical elevation-of-privilege issue. However, Chaotic Eclipse's new PoC suggests that the fix was incomplete. The researcher demonstrated that ShieldCrash can be used to circumvent the patch, potentially allowing attackers to regain the elevated access that Microsoft intended to block. While full technical details remain under embargo, the exploit reportedly leverages a logic flaw in how Defender handles certain kernel-level operations following the update.
According to the researcher, ShieldCrash exploits a race condition triggered during the cleanup phase of a terminated process. By manipulating memory allocation patterns, an attacker can force Defender into a state where the patched code path is skipped entirely. This allows malicious payloads to execute with system privileges, effectively neutralizing the protection offered by the ShieldBreak fix. The PoC has not yet been observed in active attacks, but security experts warn that it could be weaponized quickly given its straightforward implementation.
Is Microsoft Working on a Fix?
Microsoft has not yet acknowledged the ShieldCrash vulnerability publicly, though sources within the company indicate that the Microsoft Security Response Center (MSRC) is reviewing the PoC. A patch is expected to be fast-tracked if the issue is confirmed. In the meantime, organizations are advised to monitor for unusual process behavior and restrict local access wherever possible.
The emergence of ShieldCrash underscores the challenges of securing complex software like Microsoft Defender. Even well-resourced vendors can miss edge cases, and researchers continue to play a vital role in identifying gaps before they are exploited at scale.
Frequently Asked Questions
What is ShieldCrash? ShieldCrash is a newly discovered exploit that bypasses the patch for CVE-2026-69414, a high-severity Microsoft Defender vulnerability. It was revealed by researcher Chaotic Eclipse on September 9, 2026.
Has ShieldCrash been used in real attacks? No confirmed cases of ShieldCrash being used in the wild have been reported. However, the PoC is publicly available, raising concerns about potential misuse.
How can organizations protect themselves? Until a patch is released, organizations should limit local user privileges, monitor for abnormal process activity, and apply existing mitigations such as enabling Kernel DMA Protection and Credential Guard.
Comments
Leave a comment