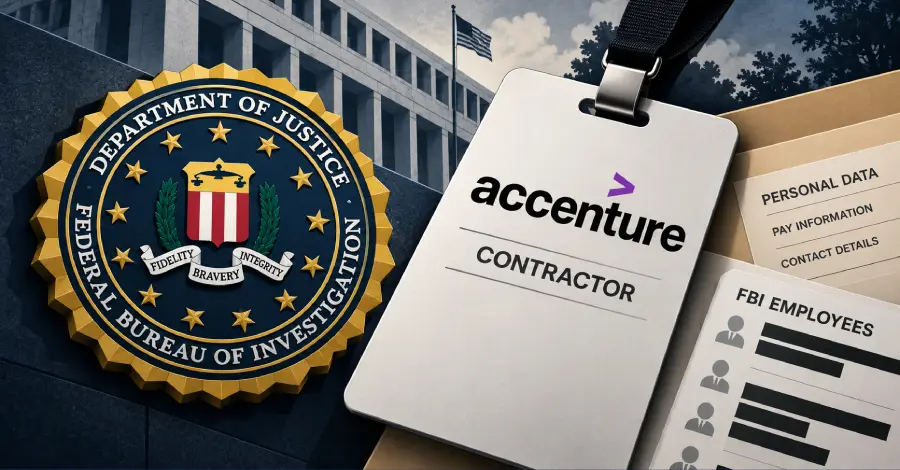
Security Oversight and Contractor Accountability
The Federal Bureau of Investigation has removed an Accenture contractor following a significant security incident involving the hacking group ShinyHunters. This breach resulted in the unauthorized exposure of personal information belonging to thousands of agency employees. The decision follows an internal review of the security failure that compromised sensitive personnel records.
Latest news
 Cybercriminals Accelerate Exploits Using Disclosed Vulnerabilities
 South Korean Authorities Investigate Potential AI Involvement in Recent Bank Hacks
 Prime Day’s Top 16 Tech Deals: Must‑Have Gadgets for Savvy Shoppers
 FBI Contractor Dismissed Following Security Breach
The incident highlights a critical lapse in data protection protocols managed by third-party vendors. Reports indicate that a failed software patch served as the primary entry point for the attackers. This vulnerability allowed the threat actors to bypass security measures and gain access to the bureau’s internal systems. The agency is now conducting a comprehensive audit to determine the full extent of the stolen data.
The FBI relies on private sector partners like Accenture to maintain complex digital infrastructure. However, this breach underscores the risks associated with external management of sensitive government databases. Experts suggest that the failure to properly implement security updates created an opening that ShinyHunters exploited with ease. The removal of the specific contractor signals a strict approach to vendor accountability regarding cybersecurity standards.
How Did the Breach Compromise Internal Systems?
The attackers targeted the infrastructure through a known vulnerability that remained unpatched. By exploiting this gap, the group successfully exfiltrated employee details before detection systems could intervene. This incident raises questions about the oversight mechanisms currently in place for contractors handling federal data. The bureau is now prioritizing the reinforcement of its digital perimeters to prevent similar unauthorized access.
The fallout from this breach will likely lead to tighter regulations for all federal technology partners. Affected employees are currently receiving guidance on how to monitor their personal information for potential identity theft. The FBI continues to investigate the scope of the exposure while working to secure its remaining vulnerable systems.
Frequently Asked Questions
What was the primary cause of the security failure? The breach occurred because a contractor failed to apply a necessary software patch, leaving a vulnerability exposed. ShinyHunters used this entry point to access employee records.
What specific information was taken in the attack? The stolen data included personal details belonging to thousands of FBI employees. The agency is currently reviewing the full extent of the compromised records.
Will there be changes to contractor security protocols? The FBI is expected to implement stricter oversight and audit requirements for all third-party vendors. This move aims to ensure that security updates are applied consistently across all systems.
Comments
Leave a comment